AI Payment Fraud Incident Response: What to Do First
What should a business do after suspected AI payment fraud?
Immediately call your bank using a verified number, ask about stopping or recovering the payment, and pause related transfers. In parallel, notify potentially applicable cyber and crime insurers, preserve evidence, secure affected accounts with qualified help, and report promptly to the FBI. Do not wait for a complete investigation.
The first minutes after discovering a fraudulent wire can determine whether money is frozen, partially recovered, or gone. Yet companies lose precious time debating whether an email was really compromised, who should call the bank, or whether the incident is serious enough to report.
AI-enabled social engineering makes that uncertainty worse. A voice clone, synthetic video, or convincing email can leave employees questioning what they saw and heard. The response should not wait for certainty. Think of it like a fire alarm: you begin protective action while someone establishes exactly what happened.
This AI payment fraud incident response guide is for Connecticut and Northeast businesses facing business email compromise, vendor impersonation, deepfake executive fraud, payroll diversion, or fraudulent wire and ACH payments. It explains the first calls, the coverage questions, the evidence to preserve, and the mistakes that can compound a loss. It also includes an emergency card you can print and complete before an incident.
Why do the first 60 minutes matter?
Criminals may move funds through several accounts quickly. Once money moves again, is converted, or leaves the country, recovery becomes harder. A fast bank notification may help the institutions involved assess a hold, recall, or other recovery action. A recall request is not a cancellation or a guarantee of recovery.
In its April 2026 summary of the 2025 Internet Crime Report, the FBI reported 22,364 AI-related complaints and nearly $893 million in associated losses. Those figures cover reported AI-related fraud, not just business payment fraud. They show why a convincing voice or video is not reliable payment authorization.
Speed also protects evidence. Email logs can change, accounts can be deleted, and attackers may continue monitoring communications. Use a trusted phone or a known-secure communication channel if company email may be compromised.
What is the immediate AI fraud response checklist?
Start these actions immediately and in parallel where possible. These are priorities, not instructions to wait. Assign an incident leader and a backup who can act if the owner or controller is unavailable.
| Priority | Owner | Action |
|---|---|---|
| Immediate | Authorized bank contact | Call the bank fraud team; ask about stopping, recalling, or recovering funds. |
| Immediate, in parallel | Finance lead | Pause related payments and verify pending beneficiary changes. |
| Immediate, in parallel | IT responder | Preserve evidence and contain access without wiping systems. |
| Promptly, in parallel | Insurance lead | Notify potentially applicable cyber and crime carriers; check approved responders. |
| As quickly as possible | Incident leader | Report to IC3 and contact the appropriate FBI office; retain report references. |
| From discovery onward | Designated recorder | Maintain a timeline, expense ledger, and next-action list. |
Who should call the bank, and what should they request?
The authorized account contact should call a known bank contact or independently verified fraud number, never one supplied in the suspicious message. Say:
“We suspect a fraudulent payment. Please escalate this to your fraud team immediately, assess available recovery actions, and give us a case number.”
Provide the transfer time, amount, currency, confirmation or trace number, originating account, receiving bank, beneficiary details, and reason fraud is suspected. Send supporting records through the bank's secure process. Do not wait for a police report before calling.
- Wire: Ask whether it can still be stopped and, if sent, whether a recall and urgent receiving-bank contact are available.
- ACH: Specify whether it was an outgoing credit or an unauthorized debit. Ask the bank which return, reversal, dispute, or protective procedures apply and their deadlines.
- Either method: Ask about related transactions and additional account safeguards. Record names, call times, case numbers, and the next follow-up.
Business account protections and payment-network procedures differ. Do not assume consumer reimbursement rules apply, or that every ACH payment can simply be reversed.
Printable payment fraud emergency card
Print this section, complete it, and store it securely offline as well as with your response plan. Use a separate secure record for account credentials; do not put passwords here.
- Incident leader / phone: ____________________
- Backup decision-maker / phone: ____________________
- Bank fraud team / verified phone: ____________________
- Authorized account contact / backup: ____________________
- Cyber insurer / policy number / claims contact: ____________________
- Crime insurer / policy number / claims contact: ____________________
- Approved IT or forensic responder / phone: ____________________
- Legal counsel / phone: ____________________
- Secure alternate communication method: ____________________
- Reporting: IC3.gov; local FBI office contact: ____________________
At discovery: Record the time, amount, payment reference, bank case number, insurer claim numbers, evidence location, and next follow-up. Call the bank; pause related payments; notify carriers; preserve and contain; report promptly.
Will cyber or crime insurance reimburse the stolen money?
A cyber policy does not automatically cover stolen funds. Coverage depends on the cause of loss, definitions, exclusions, and endorsements. A Hartford company tricked into authorizing a wire can face different coverage questions from a company whose bank receives an unauthorized instruction directly from an attacker.
| What happened? | Coverage wording to review | Important distinction |
|---|---|---|
| An employee sent money after a fake instruction. | Social engineering or fraudulent impersonation coverage | Voluntary payment induced by deception may require a specific endorsement. |
| An attacker instructed the bank without the business's authorization. | Funds transfer fraud | Definitions of fraudulent instructions and authorization matter. |
| A compromised computer system was used to cause the loss. | Computer fraud and applicable cyber coverage | Using email alone does not necessarily satisfy a computer fraud definition. |
| The business needs investigation, counsel, restoration, or notification. | Cyber incident-response coverage | Response expenses and reimbursement of stolen money are separate questions. |
These are starting points for review, not coverage promises. Check sublimits, deductibles or retentions, callback requirements, proof-of-loss deadlines, discovery and reporting provisions, exclusions, and consent requirements. A large headline cyber limit may sit above a much smaller payment-fraud sublimit.
When should cyber and crime insurers be notified?
Notify both promptly when either could apply. One carrier does not necessarily notify the other. Give a factual preliminary account: discovery time, suspected amount, affected systems, containment steps, bank contact, and any possible exposure of personal information. Update it as facts develop.
Ask about approved counsel and forensic firms before incurring major expenses when feasible. Required consent and approved-provider rules can affect reimbursement. Do not delay the bank call or necessary protective steps while assembling a perfect claim.
Before an incident, ask iConn Insurance Solutions to review your reporting instructions and payment-fraud endorsements. Call (860) 970-0977 during office hours. During an active incident, use your bank's and insurers' emergency channels directly; do not wait for an agency callback.
Should the business shut down email or payment systems?
Containment must be targeted. Wiping devices may destroy evidence; leaving a compromised account active may let criminals redirect recovery efforts. Have qualified IT personnel or insurer-approved forensic support preserve records and secure access.
Actions may include revoking sessions, resetting credentials, enforcing multifactor authentication, reviewing forwarding rules, preserving mailbox data, and isolating affected devices. If the vendor's account was compromised rather than yours, your environment may still be clean. Establish facts instead of assuming every suspicious email proves an internal breach.
What evidence should be preserved?
- Original emails with full headers and attachments.
- Voicemails, call logs, messages, meeting invitations, and lawfully available recordings.
- Bank instructions, confirmations, account activity, and beneficiary changes.
- Login, mailbox, identity, endpoint, and administrator logs.
- Approval records, callback procedures, and relevant employee accounts of events.
- Insurance applications, declarations, policies, endorsements, and carrier correspondence.
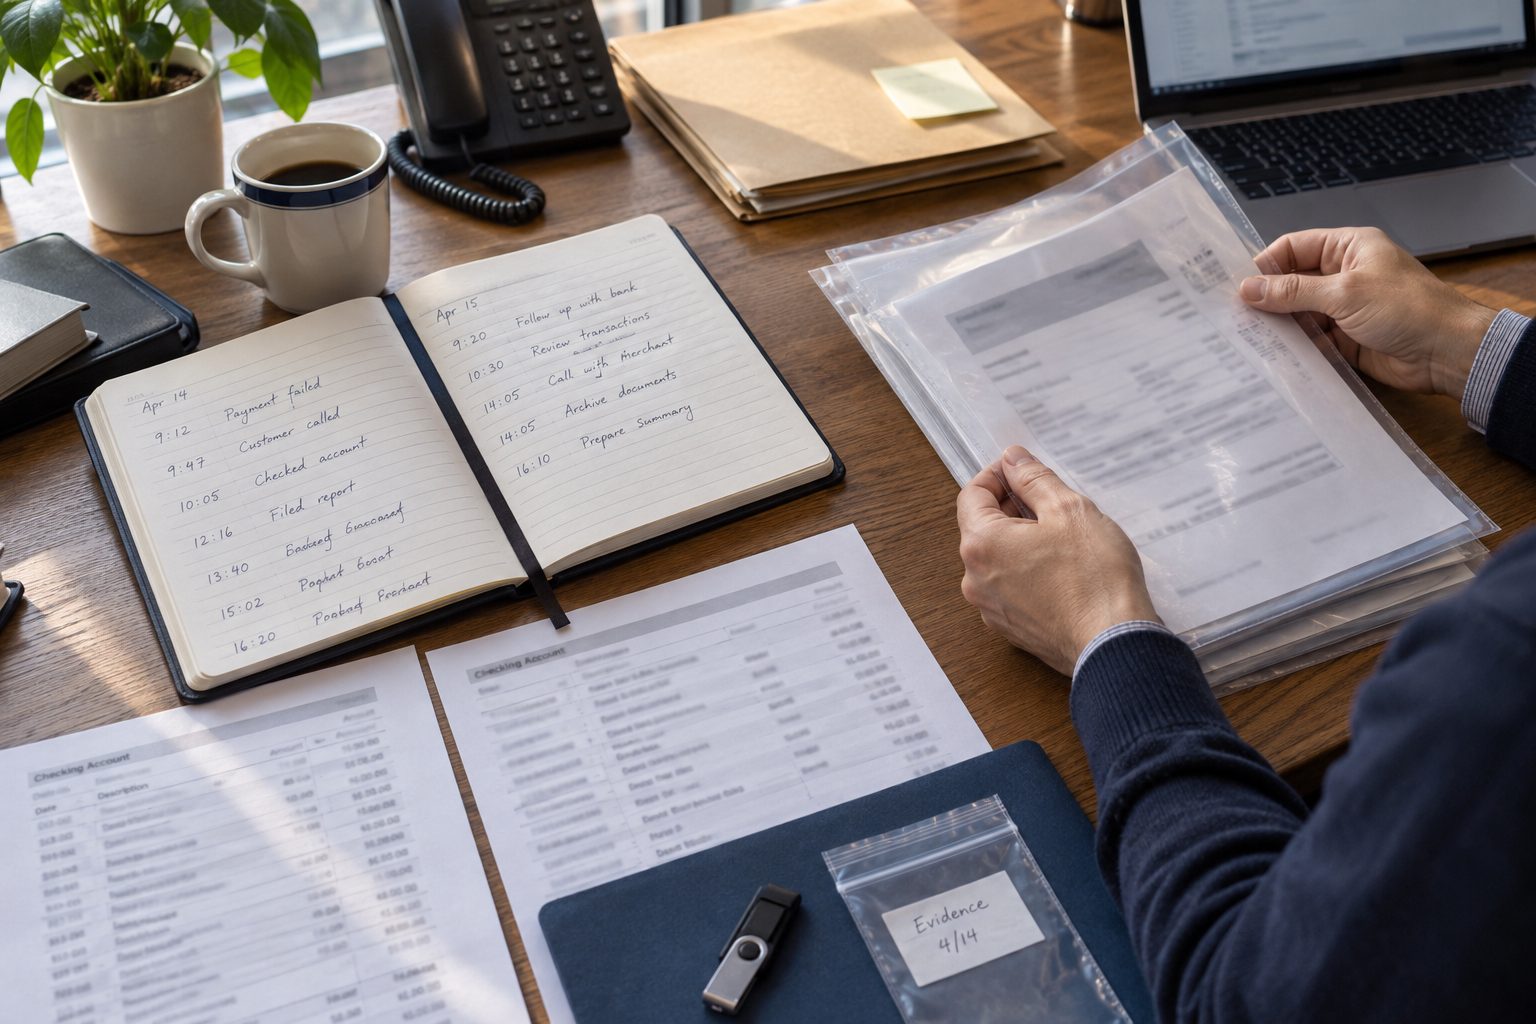
- A chronological incident log and records of expenses and recovery efforts.
Retain originals and annotate working copies. Record who collected each item and where it is stored. Interview employees calmly: ask what looked normal, what verification occurred, and when concern first appeared. A blame-first response encourages silence when fast, accurate reporting matters most.
When should law enforcement and regulators be contacted?
Report online payment fraud to the FBI's Internet Crime Complaint Center as quickly as possible. Contact the appropriate FBI office and, where appropriate, local police. Retain submission references and update reports as information develops. Reporting does not guarantee recovery.
Payment fraud and a legally reportable personal-information breach are different questions. Under Connecticut Attorney General guidance, covered consumer notices must be made without unreasonable delay and no later than 60 days after discovery; the Attorney General must be notified no later than residents. The guidance also describes 24 months of credit monitoring when a resident's Social Security or taxpayer identification number is believed compromised.
Those are not reasons to wait. Counsel should assess the specific facts, statutory requirements and exceptions, and other applicable obligations. Connecticut, New York, Rhode Island, and Massachusetts have different requirements; affected residents' locations matter, not just your headquarters. Avoid unsupported public conclusions or promises of reimbursement.
How do you prevent a second payment?
Attackers may claim the first payment failed or impersonate the bank, insurer, attorney, or police. Pause affected beneficiary payments, independently verify pending account changes, review payroll instructions, and require dual approval for exceptions. Use established vendor contacts, not the suspicious conversation.
A Fairfield County business should treat a supposed recovery agent's urgent request for a new transfer as another verification problem, not proof help has arrived. Never rely on a familiar voice alone.
What could this cost out of pocket?
Track stolen funds, recovered amounts, bank charges, legal and forensic fees, overtime, replacement payments, restoration, and business interruption in a dedicated ledger. Keep invoices, approvals, engagement letters, and proof of payment. Not every expense is insured.
Your exposure may include unrecovered money above a sublimit, deductibles, excluded losses, and expenses incurred without required consent. For illustration, a $500,000 loss with a $100,000 applicable sublimit leaves at least $400,000 outside that limit before considering recoveries, deductibles, or other coverage. That is arithmetic, not a claim estimate.
What happens during the first seven days?
- Day 1: Continue recovery efforts, containment, insurer notice, reporting, and evidence preservation.
- Days 2–3: Establish affected systems, vendors, payments, and information. Confirm legal notice obligations and update carriers.
- Days 4–7: Restore secure payment processes, document costs, communicate verified facts, and close urgent control gaps.
Do not force a final conclusion to meet a timetable. Afterwards, review callbacks, dual approval, transaction limits, executive exceptions, monitoring, and training. Compare actual practices with representations made to insurers and test the revised plan with a tabletop exercise.
Why do independent brokers matter after a fraud event?
An independent broker can coordinate notice across policies and compare coverage beyond price. Multi-carrier access, regional market knowledge, personalized service, and a well-documented submission can help you assess renewal options after control improvements. The broker does not replace the bank, counsel, forensic specialists, or adjuster and cannot guarantee coverage.
iConn Insurance Solutions can help organize that review. For related business insurance guidance, visit sister site Insure Connecticut LLC. Insure Connecticut LLC, iConn Insurance Solutions, and Wealth America, Inc. are independently operated companies under common ownership.
Frequently Asked Questions About Responding to AI Payment Fraud
What is the first call after a fraudulent wire?
Call your financial institution using a verified number and request immediate fraud-team escalation. Ask what stopping or recovery options remain. In parallel, assign others to notify potentially applicable insurers, preserve evidence, and report promptly to the FBI. Do not wait for a completed internal investigation.
How much can a bank recover after wire fraud?
Recovery depends on timing, destination, remaining funds, bank cooperation, and whether the money moved again. There is no guaranteed amount. A recall request does not cancel a completed transfer automatically. Contact the bank immediately and document each follow-up rather than assuming submission means recovery.
How much could payment fraud cost our business?
Potential costs include stolen funds, investigation, counsel, interruption, and recovery expenses. Insurance may leave deductibles, excluded costs, or losses above a sublimit. There is no reliable universal price. Estimate exposure from your payment sizes and actual policy wording, then separately track every incident expense.
Should we notify insurance before knowing exactly what happened?
Prompt factual notice is generally safer than waiting for a complete investigation. Describe what is known and what remains uncertain, then update each potentially applicable carrier. Check the actual policies for reporting deadlines, required consent, approved providers, and proof-of-loss requirements. Notification alone does not establish coverage.
What Connecticut reporting rules apply?
A fraudulent payment is not automatically a reportable personal-information breach. For covered breaches, Connecticut guidance requires consumer notice without unreasonable delay and generally no later than 60 days after discovery, with Attorney General notice no later than resident notice. Have counsel evaluate applicability and other duties promptly.
How should we choose payment-fraud insurance?
Compare social engineering, funds transfer fraud, computer fraud, and incident-response wording rather than the cyber policy's headline limit alone. Ask about sublimits, deductibles, verification conditions, exclusions, notice, and approved providers. An independent broker can compare options against your typical transactions and documented payment controls.
Prepare the response before the money moves
A fast response cannot guarantee recovery, but a rehearsed plan reduces avoidable delay. Complete the emergency card and test who acts when your primary decision-maker is unavailable.
Ask iConn Insurance Solutions for a cyber and crime policy review. Call (860) 970-0977 to arrange a secure way to provide declarations and endorsements. Review payment-fraud limits, reporting instructions, and verification requirements before the next urgent payment request arrives.
This guide is general information, not legal advice or a coverage determination. Actual policies and applicable law control.
Related Content
Is Your Trucking ELD Still Legal? Five Devices FMCSA Revoked in August 2026
The October 6, 2026 replacement deadline for five revoked ELDs has passed. Connecticut fleets should verify device status, correct noncompliance, and document the fix.
Read post →
AI Privacy, Bodily Injury, and Property Damage: The Exposures Businesses Miss
AI liability is not limited to wrong answers. Privacy, bodily injury, and property damage claims can arise when people act on AI outputs.
Read post →
Generative AI Insurance: The Coverage Gap Businesses Need to Know
Generative AI is already in customer support, marketing, operations, and professional services. Here is why businesses deploying AI should review third-party liability exposure now.
Read post →
AI Hallucinations and Bad Outputs: The Liability Problem Behind Confident Wrong Answers
AI hallucinations can become liability claims when customers, clients, vendors, or users rely on confident wrong answers and suffer financial loss.
Read post →